

Using the Salesforce Connection Manager
The Salesforce Connection Manager is an SSIS connection manager that can be used to establish connections with the Salesforce Server. It allows you to specify how you want to connect to Salesforce.com.
To add a Salesforce connection to your SSIS package, right-click in the Connection Managers area, and choose "New Connection..." from the context menu.
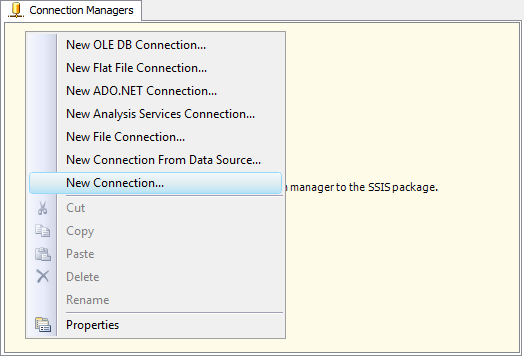
You will be prompted with the following window, where you can choose the "Salesforce (KingswaySoft)" or "Salesforce" (deprecated) item to add the connection.

Note that since v7.0 release, you can see two Salesforce connection managers available from us in the list. We recommend you use the "Salesforce (KingswaySoft)" one to avoid any potential conflicts with other vendor solutions. The two connection manager types work exactly the same, but the "Salesforce" one is now considered a deprecated connection after the v7.0 release.
Salesforce Connection Manager contains the following pages for configuring how to connect to the Salesforce service:
- Connection
- Proxy Server
- Advanced Settings
- More Info
Connection Page
The Connection page of Salesforce Connection Manager allows you to specify the general settings of the connection. The connection supports two service endpoints - SOAP and REST.
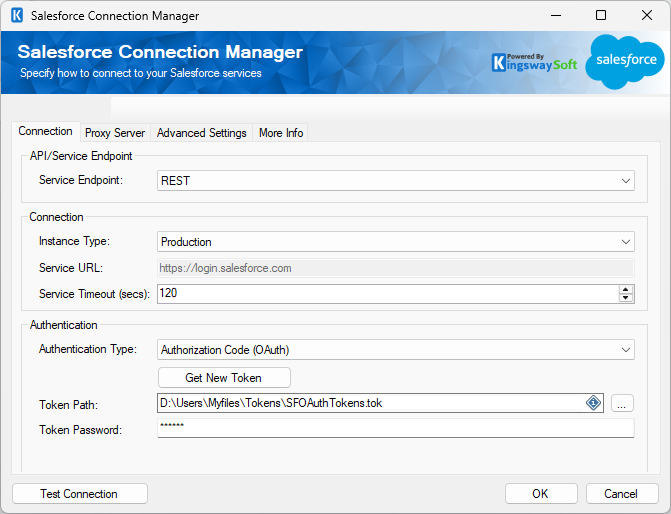
- API/Service Endpoint
-
- Service Endpoint
-
The Service Endpoint option allows you to specify the API you want to connect to Salesforce with. There are two options available:
- SOAP
- REST
Note: OAuth authentication with the SOAP service endpoint is available since v25.2.
- Connection
-
- Instance Type
-
The Instance Type option allows you to specify what Salesforce instance you are connecting to. The following options are available:
- Production
- Sandbox
- Other
For Production and Sandbox instances, the Service URL option below is automatically populated. When the "Other" option is selected, you can specify an alternate Service URL, such as when connecting to a Salesforce instance using a custom domain.
- Service URL
-
The Service URL option allows you to specify the URL that will be used to connect to your Salesforce instance. This field is automatically populated for Production and Sandbox instances and can be edited when the Instance Type option is set to "Other".
- Service Timeout (secs)
-
The Service Timeout (secs) option allows you to specify the maximum number of seconds that the Salesforce Connection Manager will wait while trying to establish a connection with the Salesforce service.
- Authentication
-
- Authentication Type
-
This option allows you to specify the preferred type of authentication you want to use when connecting to Salesforce. The following options are available:
- Authorization Code (OAuth)
- Client Credentials with Certificate (OAuth)
- Client Credentials (OAuth, Server-to-Server Authentication) (since v26.1)
- Client Credentials with Username and Password (OAuth)
- Legacy SOAP Login Method (available in v25.2 and earlier)
- Authorization Code Authentication Type:
-
- Get New Token
-
This button completes the OAuth authentication process in order to generate a new token.

- Client Id: The Client Id option allows you to specify the unique ID that identifies the application making the request.
- Client Secret: The Client Secret option allows you to specify the client secret belonging to your app.
- Redirect Uri: The Redirect Uri option allows you to specify the redirect URI used to complete the authentication process.
- Prevent cross-site request forgery (CSRF) exploits: Cross-site request forgery (CSRF) is an attack that can cause the user to perform unwanted actions on web pages the user is authenticated on. The option is turned on by default and can be turned off if necessary.
- PKCE (Enhanced Security): PKCE (Proof Key for Code Exchange) ensures that the client that initiates the OAuth flow is the same client that completes the flow. The corresponding PKCE option would need to be configured in Salesforce.
- App Type (available in v26.1 and earlier)
-
Note: Starting with v26.2, the App Type selection is no longer displayed. The KingswaySoft App option has been discontinued, and users must provide credentials from their own Salesforce application for Authorization Code authentication. As recommended by Salesforce, an External Client App (ECA) can be created in your instance for OAuth authentication. For more details on creating an ECA and generating the necessary credentials, please refer to our Setting Up Modern OAuth Connections for Salesforce blog post.
- KingswaySoft App (since v25.1)
-
The KingswaySoft OAuth app is a publicly shared app that was provided so that you could test our software without going through the process of creating an app. It was not recommended for production use, as we could not guarantee that our app would always be available. Support for the KingswaySoft App was discontinued starting with v26.2.
- My Own App
-
Selecting this option allows you to use your own Client ID and Secret to connect to Salesforce.
- Token Path
-
The path to the token file on the file system.
- Token Password
-
The password to the token file.
- Client Credentials with Certificate Authentication Type:
-
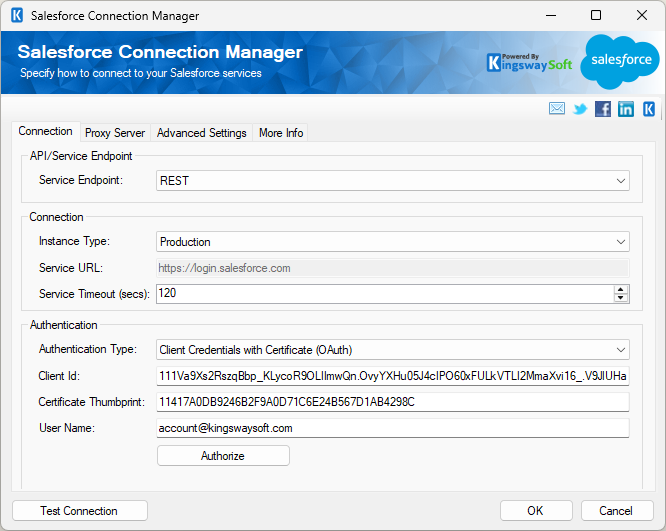
For the Client Credentials with Certificate mode, you will need to generate a Public/Private Key Pair.
- Download and install OpenSSL for Windows. Note that you may need to restart your machine after installation.
- Launch Windows Command Prompt as an administrator using the "Run as administrator" option.
- In the command prompt window, navigate to the bin folder of the installation location of OpenSSL, e.g., "cd C:\OpenSSL-Win32\bin".
- Execute the following commands. Note that the second command will prompt you to enter a password twice. From the generated files:
- certificate.pem: This is the Public Key file that is going to be uploaded to your Salesforce App.
- public_privatekey.pfx: This is the Private Key file that is going to be installed locally on the machine for signing JWT.
openssl req -x509 -newkey rsa:2048 -sha256 -keyout privatekey.pem -out certificate.pem -days 1825 -nodes -subj "/CN=SalesforceJWT"
openssl pkcs12 -export -out public_privatekey.pfx -inkey privatekey.pem -in certificate.pem
The public certificate will need to be uploaded into your Salesforce App under Settings, Flow Enablement. Note that External Client Apps require the file to be .PEM. While in the settings, you would also need to click Enable JWT Bearer Flow.

- Client Id
-
The Client Id option allows you to specify the unique identifier that identifies the application making the request. Within your Salesforce App, this would be the generated Consumer Key.
- Certificate Thumbprint
-
The Certificate Thumbprint option allows you to specify the thumbprint of the certificate created for the application you have created.
- User Name
-
The User Name option allows you to specify the user account used to connect to Salesforce.com for your integration purposes.
- Authorize Button
-
By clicking the Authorize button, a window pops up to help you authorize the application to access your Salesforce data. All you need to do is to provide the Redirect URL depending on the client application. When working with an External Client App, the Authorize step is not required and may be ignored.
- Client Credentials (OAuth, Server-to-Server Authentication) (since v26.1):
-
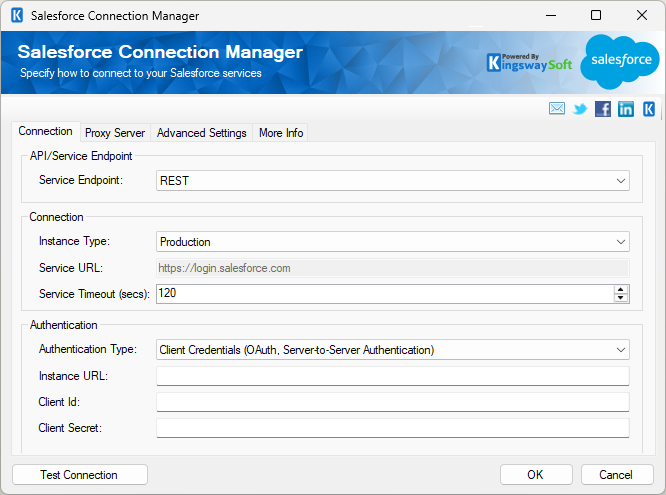
- Instance URL
-
The Instance URL is the base URL of your Salesforce organization.
- Client Id
-
The Client Id option allows you to specify the unique ID that identifies the application making the request.
- Client Secret
-
The Client Secret option allows you to specify the client secret belonging to your app.
- Client Credentials with Username and Password Authentication Type:
-
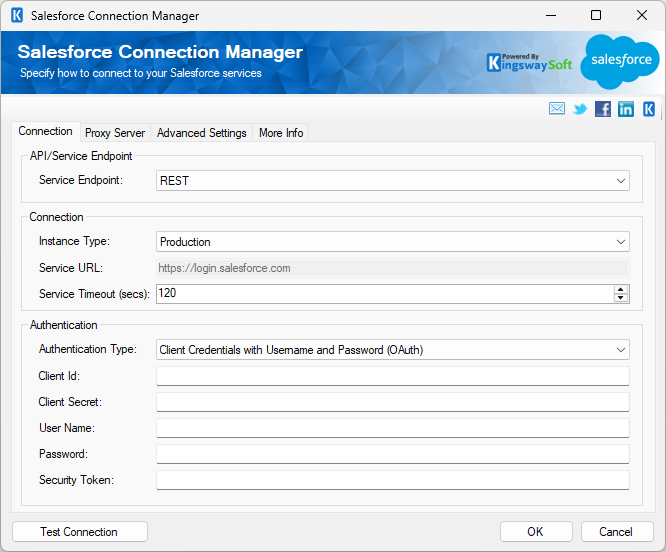
Note: This authentication type requires a Salesforce Connected App, as the OAuth 2.0 username-password flow is not supported by External Client Apps. Salesforce has announced that the OAuth 2.0 username-password flow for Connected Apps will be retired on February 20, 2027.
- Client Id
-
The Client Id option allows you to specify the unique ID that identifies the application making the request.
- Client Secret
-
The Client Secret option allows you to specify the client secret belonging to your app.
- User Name
-
The User Name option allows you to specify the user account used to connect to Salesforce.com for your integration purposes.
- Password
-
The Password option allows you to specify a password for the above user in order to be able to log in to the Salesforce service.
- Security Token
-
The Security Token option is used to specify the security token that you have requested in Salesforce.com. If you do not have a security token yet, you must request one by resetting your security token. To do so, log in to Salesforce.com, click Your Name | My Settings | Personal | Reset Security Token, and then click the Reset My Security Token button. The new security token is sent via email to the email address on your Salesforce user record. Note that there is no way to retrieve your security token from Salesforce. In case you have lost it, you must request a new one by resetting it. If you ever need to do so, make sure that you update the security token setting of any other applications that might be using the same authentication.
- Legacy SOAP Login Method (available in v25.2 and earlier):
-
Note: The Legacy SOAP Login authentication type is no longer available starting with v26.1, following the update of Salesforce API support to v66.0. Salesforce has also announced that the SOAP API login() method in earlier supported API versions will be retired with the Summer '27 release. If you are using v25.2 or earlier with Legacy SOAP Login, you should transition to one of the OAuth authentication options above before this retirement. For more information, please refer to our Setting Up Modern OAuth Connections for Salesforce blog post.
- User Name
-
The User Name that you use to connect to your Salesforce account.
- Password
-
The password for the above user, required to log in to the Salesforce service.
- Security Token
-
The Security Token option is used to specify the security token that you have requested in your Salesforce instance. You can follow the above steps from the Client Credentials with Username and Password Authentication Type section to get a security token if you do not have one.
- Test Connection
-
After you have provided all connection information, you may click the "Test Connection" button to test if you can successfully log in to Salesforce.
Proxy Server Page
The Proxy Server page of Salesforce Connection Manager allows you to specify a proxy server in order to connect to the Salesforce service.

- Proxy Server Settings
-
- Proxy Mode (since v6.0)
-
The Proxy Mode option allows you to specify how you want to configure the proxy server settings. The following options are available:
- No Proxy
- Auto-detect (Using system-configured proxy)
- Manual
- Proxy Server
-
Using the Proxy Server option, you can provide a proxy server to connect to Salesforce.com.
- Port
-
The Port option allows you to specify the port number of the proxy server for the connection.
- Username (Proxy Server Authentication)
-
The Username option (under Proxy Server Authentication) allows you to specify the proxy user account.
- Password (Proxy Server Authentication)
-
The Password option (under Proxy Server Authentication) allows you to specify the proxy user's password.
Note: The Proxy Password is not included in the connection manager's ConnectionString property by default. This is by design for security reasons. However, you can include it in your ConnectionString if you want to parameterize your connection manager. The format would be ProxyPassword=myProxyPassword; (make sure you have a semicolon as the last character). It can be anywhere in the ConnectionString.
Advanced Settings Page
The Advanced Settings page of Salesforce Connection Manager allows you to specify some advanced options when connecting to the Salesforce service.

- Optional Headers
-
- Allow Save on Duplicate
-
When this option is enabled, the service calls made to Salesforce will contain a header option that indicates that duplicates are allowed.
- Allow Field Truncation
-
When this option is enabled, the service calls made to Salesforce will contain a header option that indicates that field truncation is allowed.
- Assignment Rule
-
Using this option, you can specify the assignment rule to be fired when a lead or case is created using the Salesforce destination component. The input of this field should be the ID of the assignment rule in Salesforce. You can get an assignment rule's ID by navigating to the assignment rule record in Salesforce: the ID should be the last part of the URL, which generally consists of 18 characters.
- Use Default Assignment Rule (since v8.0)
-
This option allows you to use the default (active) assignment rule for a Case/Lead or apply all territory assignment rules to the Account.
- Advanced Error Handling
-
- Retry on Intermittent Errors
-
This is an option designed to help recover from possible intermittent outages or disruption of service, so the integration does not have to be stopped because of such temporary issues. Enabling this option will allow service calls to be retried upon certain types of failure. A service call may be retried up to 3 times before an exception is fired. Retries occur after 0 seconds, 15 seconds, and 60 seconds.
Warning: Although we have designed our retry feature carefully so that the retry should only happen when it is deemed to be safe to do so. However, on some occasions, such retry service calls could result in the creation of duplicate data.
More Info Page
The More Info page shows some basic information about the toolkit. On this page, you can find the version information of the toolkit.
